PHP and Node.js vulnerabilities: ZEIT.IO is not affected
 Robert Reiz | October 22, 2026 | 09:47 UTC
Wednesday morning, just after eight. Sabine runs an agency with twelve people, and she's reading the news over her first coffee. The headline: "php2shell – critical vulnerabilities allow code injection in PHP". Two flaws, both rated 9.2 out of 10, affecting every PHP version since PHP 5. A few lines further down: Node.js has just fixed ten security vulnerabilities as well, four of them rated "high".
Sabine's first thought is her agency's data: timesheets, invoices, contracts with hourly rates, her freelancers' bank details. Is all of that sitting on a server that's vulnerable right now?
At ZEIT.IO, the answer is no.
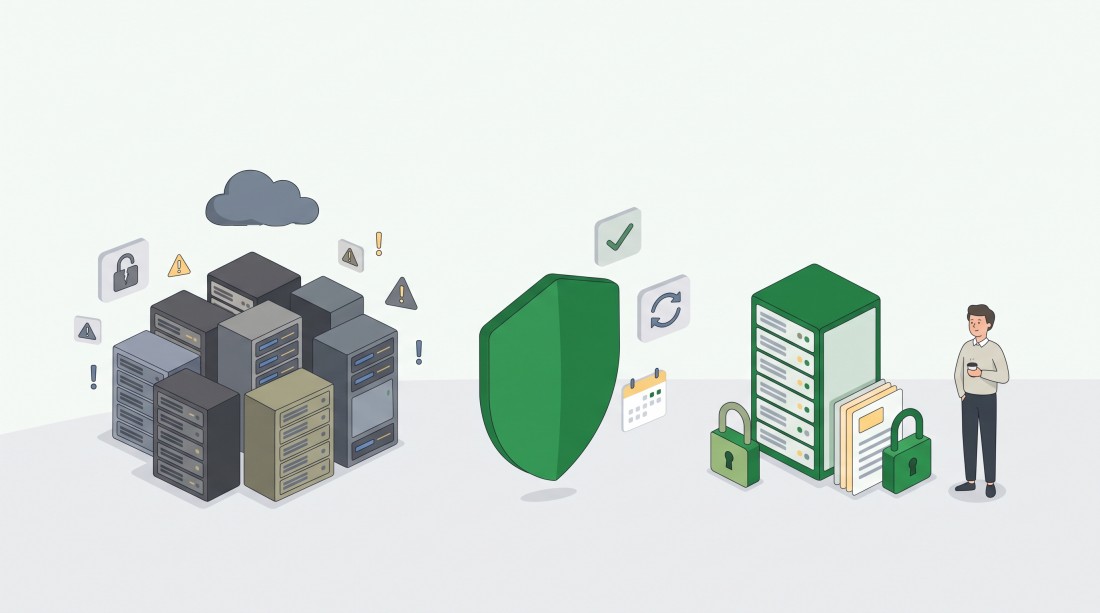
ZEIT.IO runs neither PHP nor Node.js on its servers. The vulnerabilities reported this week do not affect our platform or your data.
What the news is about
On 21 October, the PHP project released updates for two critical vulnerabilities that have become known as php2shell. They let attackers run their own code on a web server over the network – without logging in, just by sending crafted requests. Practically every server running PHP is affected, along with many routers, NAS systems and firewalls whose admin interface is built on PHP. At almost the same time, Node.js closed vulnerabilities in TLS certificate checking, name resolution and the decompression of compressed data, among others.
PHP and Node.js power a large part of the internet. So the concern is big – and asking whether your own service providers are affected is exactly the right question.
What this means for ZEIT.IO
No PHP, no Node.js on our servers
Neither PHP nor Node.js is installed on the servers that process and store your data. We didn't answer this from memory: after the reports came out, we specifically checked our server images.
A vulnerability in software that isn't there can't be exploited. For you, that means:
- There is nothing you need to do in ZEIT.IO.
- There was no point in time when your data with us was exposed through these vulnerabilities.
- Time tracking, invoices, contracts and receipts carry on as normal.
Weekly security checks
Not being affected this time isn't luck we rely on. Every week, we run automated checks of our code and every software library we use against known security vulnerabilities. When a new flaw turns up, we see it – and act before it becomes a problem.
Security updates every week – automatically
The operating system components of our servers are updated every week, too. That way security patches reach our systems regularly and automatically, without someone first having to read a news item and step in by hand. If tomorrow a vulnerability is found in a component we actually use, it will normally be closed within a few days.
To be honest
No software in the world is free of bugs – ours included. That's exactly why we don't count on never being affected. We count on being fast: check regularly, update regularly, respond immediately when needed.
And part of your security is in your own hands. Turn on two-factor authentication in your user settings – it protects your account even if a password ever ends up in the wrong hands.
A tip beyond ZEIT.IO: check whether your office runs devices with a PHP-based web interface – a NAS, a router or a firewall, for example – and install the manufacturer's updates there. The same goes for your own website, for instance if it runs on WordPress.
Why this matters
ZEIT.IO doesn't hold just any data. It holds your hourly rates, your contracts, your invoices and the bank details of your customers and suppliers. You're trusting us with part of your business. We don't earn that trust with promises, but week after week with routine: lean technology, regular checks and updates that never pile up.
While others spend this Wednesday frantically patching servers, Sabine can finish her coffee in peace.
Your data is safe with us.